
VEHERE
NETWORK DETECTION AND RESPONSE (NDR)
AND FULL PACKET CAPTURE (PCAP)
Vehere is a new-age cyber defense software company specializing in AI Cyber Network Intelligence. Powerful and scalable AI-powered network intelligence platform processes petabytes of network data at terabit speed to detect threats in real-time, identify attack patterns, and enable fast, effective response with precision.
Today, cybersecurity teams across Fortune 500 enterprises and critical infrastructure environments, including global telecom operators, financial institutions, and smart cities, rely on Vehere for deep network visibility and protection against advanced and evasive cyberattacks.
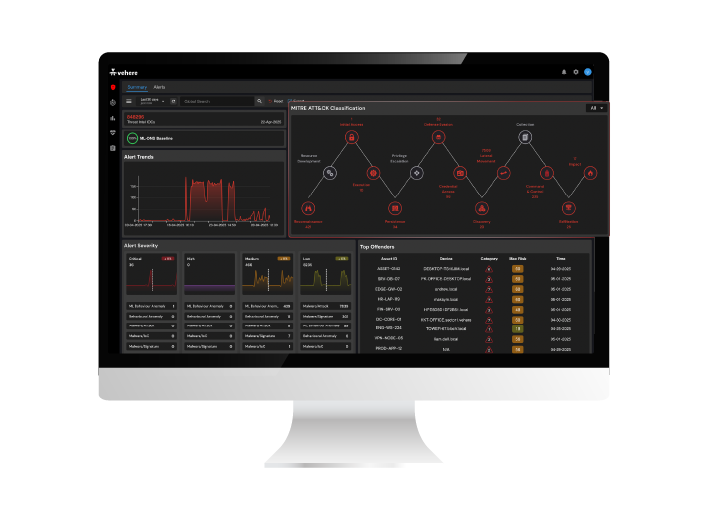
Why VEHERE?
- AI-powered Hunting, Detection and Response
- Widest threat coverage
- Full, Continuous Packet Capture
- Built-in PCAP analysis tool
- Native IDS with true real-time, line rate threat detection
- Built-in PII Masking
- SIGINT grade threat protection
- Native On-demand dynamic file analysis for instant verdict on suspicious files
- Custom queries
- Extremely Scalable
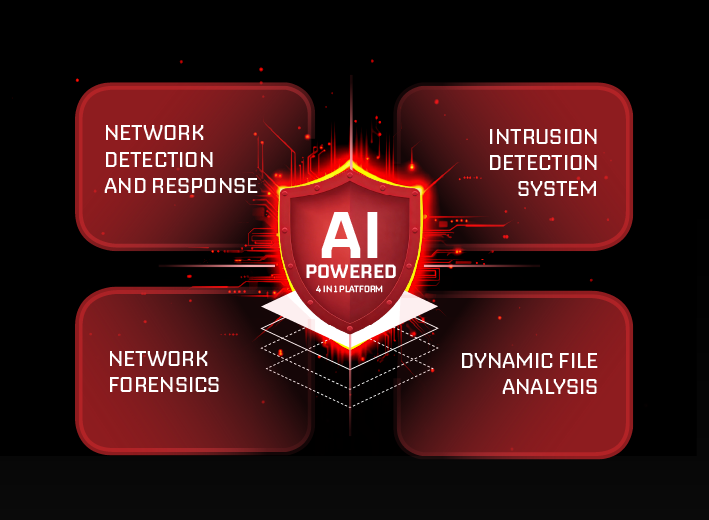
BUILT FOR COMBAT, ENGINEERED FOR SCALE, ON-PREMISES BY DESIGN

Visibility across internal and external network traffic, Lossless Packet Capture

High-speed threat hunting across terabit traffic and petabyte-scale data, identifying patterns and anomalies

Built-in malware sandbox to detects zero-day malware

Frictionless investigation to real-time alerts in minutes by live and historical network traffic analysis
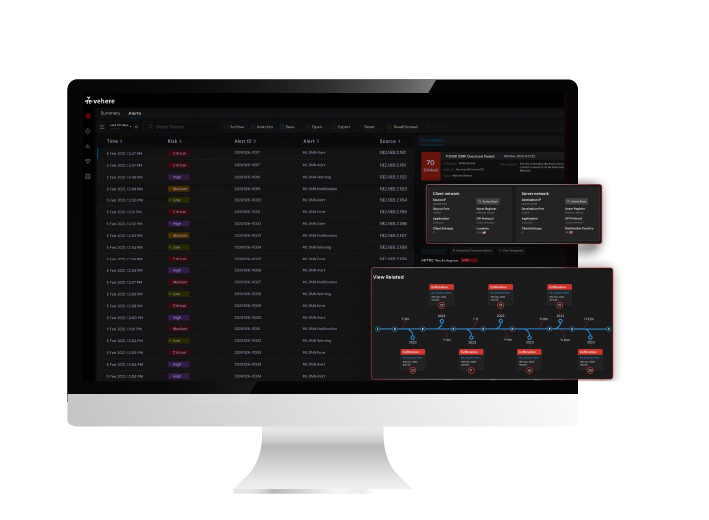
BATTLE-TESTED NETWORK DETECTION AND RESPONSE
- AI-powered behavioral anomaly detection
- ML generated alert rationale
- Line rate detection
- Full, continuous packet capture
- Built-in and external threat intelligence
- Patent-pending Indexed-Raw technique for faster retrieval of packets
- Encrypted traffic analysis
- Multi-Agent AI for autonomous threat detection, hunting and response
- Native PCAP viewer
- Full-packet session reconstruction
- On-demand dynamic file analysis
CAPTURE EVERY PACKET. RECONSTRUCT EVERY ATTACK. ZERO BLIND SPOTS AT PETABYTE SCALE.
- Full fidelity packet capture (PCAP) for deep investigation
- Full session reconstruction to rebuild attacker timelines
- Metadata extraction from real network traffic
- Encrypted traffic intelligence without decrypting payloads
- Evidence preservation suitable for legal, audit, and IR workflows
STRENGTHENING DIGITAL RESILIENCE FROM NATIONS TO ENTERPRISES
- Government and Public Sector
- Banking and Financial Institutions
- Telecom and Network Providers
- Cloud, Data & IT Services
- Critical Infrastructure
Want to buy or try a solution?
Leave your contact details now, and we’ll contact you as soon as possible.
Discover Solutions in Detail
Download the latest presentation to explore the solutions’ capabilities, real-life use cases, and key advantages, and learn how they can strengthen your security posture.